apache/casbin is tracked by TopGit as a security tool, with 20.5k stars on GitHub, written primarily in Go. Apache Casbin: an authorization library that supports access control models like ACL, RBAC, ABAC.
Snapshot summary built from the project's own GitHub metadata — there's no written TopGit review yet. The page will update automatically when a full review is published.
WHY NO REVIEW YET
TopGit writes full reviews for the most-starred, most-requested repositories. This page is a snapshot until then — see the READ ME tab for the original README in full.
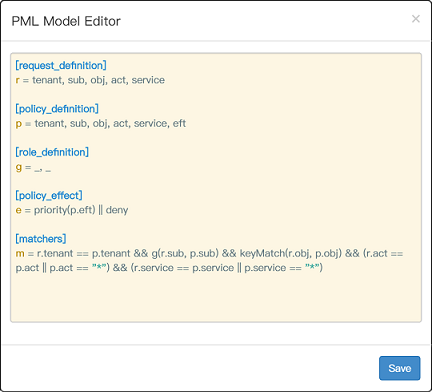
News: still worry about how to write the correct Apache Casbin policy? Apache Casbin online editor is coming to help! Try it at: https://casbin.apache.org/editor/
Apache Casbin is a powerful and efficient open-source access control library for Golang projects. It provides support for enforcing authorization based on various access control models.
All the languages supported by Apache Casbin:
Casbin
jCasbin
node-Casbin
PHP-Casbin
production-ready
production-ready
production-ready
production-ready
PyCasbin
Casbin.NET
Casbin-CPP
Casbin-RS
production-ready
production-ready
production-ready
production-ready
Table of contents
Supported models
How it works?
Features
Installation
Documentation
Online editor
Tutorials
Get started
Policy management
Policy persistence
Policy consistence between multiple nodes
Role manager
Benchmarks
Examples
Middlewares
Our adopters
Supported models
ACL (Access Control List)
ACL with superuser
ACL without users: especially useful for systems that don't have authentication or user log-ins.
ACL without resources: some scenarios may target for a type of resources instead of an individual resource by using permissions like write-article, read-log. It doesn't control the access to a specific article or log.
RBAC (Role-Based Access Control)
RBAC with resource roles: both users and resources can have roles (or groups) at the same time.
RBAC with domains/tenants: users can have different role sets for different domains/tenants.
ABAC (Attribute-Based Access Control): syntax sugar like resource.Owner can be used to get the attribute for a resource.
RESTful: supports paths like /res/*, /res/:id and HTTP methods like GET, POST, PUT, DELETE.
Deny-override: both allow and deny authorizations are supported, deny overrides the allow.
Priority: the policy rules can be prioritized like firewall rules.
How it works?
In Casbin, an access control model is abstracted into a CONF file based on the PERM metamodel (Policy, Effect, Request, Matchers). So switching or upgrading the authorization mechanism for a project is just as simple as modifying a configuration. You can customize your own access control model by combining the available models. For example, you can get RBAC roles and ABAC attributes together inside one model and share one set of policy rules.
The most basic and simplest model in Casbin is ACL. ACL's model CONF is:
Further more, if you are using ABAC, you can try operator in like following in Casbin golang edition (jCasbin and Node-Casbin are not supported yet):
# Matchers
[matchers]
m = r.obj == p.obj && r.act == p.act || r.obj in ('data2', 'data3')
But you SHOULD make sure that the length of the array is MORE than 1, otherwise there will cause it to panic.
For more operators, you may take a look at govaluate
Features
What Apache Casbin does:
enforce the policy in the classic {subject, object, action} form or a customized form as you defined, both allow and deny authorizations are supported.
handle the storage of the access control model and its policy.
manage the role-user mappings and role-role mappings (aka role hierarchy in RBAC).
support built-in superuser like root or administrator. A superuser can do anything without explicit permissions.
multiple built-in operators to support the rule matching. For example, keyMatch can map a resource key /foo/bar to the pattern /foo*.
What Apache Casbin does NOT do:
authentication (aka verify username and password when a user logs in)
manage the list of users or roles. I believe it's more convenient for the project itself to manage these entities. Users usually have their passwords, and Apache Casbin is not designed as a password container. However, Apache Casbin stores the user-role mapping for the RBAC scenario.
Installation
go get github.com/casbin/casbin/v3
Documentation
https://casbin.apache.org/docs/overview
Online editor
You can also use the online editor (https://casbin.apache.org/editor/) to write your Casbin model and policy in your web browser. It provides functionality such as syntax highlighting and code completion, just like an IDE for a programming language.
Tutorials
https://casbin.apache.org/docs/tutorials
Get started
New a Casbin enforcer with a model file and a policy file:
e, _ := casbin.NewEnforcer("path/to/model.conf", "path/to/policy.csv")
Note: you can also initialize an enforcer with policy in DB instead of file, see Policy-persistence section for details.
Add an enforcement hook into your code right before the access happens:
sub := "alice" // the user that wants to access a resource.
obj := "data1" // the resource that is going to be accessed.
act := "read" // the operation that the user performs on the resource.

if res, _ := e.Enforce(sub, obj, act); res {
    // permit alice to read data1
} else {
    // deny the request, show an error
}
Besides the static policy file, Apache Casbin also provides API for permission management at run-time. For example, You can get all the roles assigned to a user as below:
roles, _ := e.GetImplicitRolesForUser(sub)
See Policy management APIs for more usage.
Policy management
Apache Casbin provides two sets of APIs to manage permissions:
Management API: the primitive API that provides full support for Apache Casbin policy management.
RBAC API: a more friendly API for RBAC. This API is a subset of Management API. The RBAC users could use this API to simplify the code.
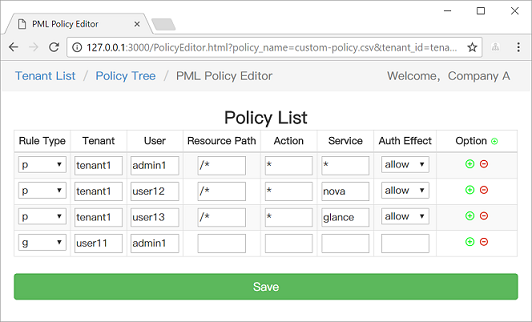
We also provide a web-based UI for model management and policy management:
Policy persistence
https://casbin.apache.org/docs/adapters
Policy consistence between multiple nodes
https://casbin.apache.org/docs/watchers
Role manager
https://casbin.apache.org/docs/role-managers
Benchmarks
https://casbin.apache.org/docs/benchmark
Examples
Model
Model file
Policy file
ACL
basic_model.conf
basic_policy.csv
ACL with superuser
basic_model_with_root.conf
basic_policy.csv
ACL without users
basic_model_without_users.conf
basic_policy_without_users.csv
ACL without resources
basic_model_without_resources.conf
basic_policy_without_resources.csv
RBAC
rbac_model.conf
rbac_policy.csv
RBAC with resource roles
rbac_model_with_resource_roles.conf
rbac_policy_with_resource_roles.csv
RBAC with domains/tenants
rbac_model_with_domains.conf
rbac_policy_with_domains.csv
ABAC
abac_model.conf
N/A
RESTful
keymatch_model.conf
keymatch_policy.csv
Deny-override
rbac_model_with_deny.conf
rbac_policy_with_deny.csv
Priority
priority_model.conf
priority_policy.csv
Middlewares
Authz middlewares for web frameworks: https://casbin.apache.org/docs/middlewares
Our adopters
https://casbin.apache.org/docs/adopters
How to Contribute
Please read the contributing guide.
Contributors
This project exists thanks to all the people who contribute.
Star History
License
This project is licensed under the Apache 2.0 license.
Contact
If you have any issues or feature requests, please contact us. PR is welcomed.
The most recent commit recorded on apache/casbin was 3 months ago, based on the GitHub push timestamp. The repository has 1.8k forks — one of the better signals of community interest.
How many stars does apache/casbin have?
apache/casbin has 20.5k GitHub stars — refresh the page for the live number, or check github.com/apache/casbin. TopGit mirrors GitHub's count but does not claim minute-by-minute accuracy.
What else is in the Security space?
apache/casbin is tracked by TopGit under the Security category, alongside 18 GitHub-tagged topics. Trending and Topics pages list peer repositories of comparable stars and language.
What language is apache/casbin written in?
apache/casbin is written primarily in Go. GitHub's language field is based on the largest share of bytes in the default branch.
This TopGit page is a snapshot — the READ ME tab shows the project's own README content (links stripped, images preserved). The GitHub repository at github.com/apache/casbin is the definitive source.
Why is apache/casbin categorized under Security?
TopGit places apache/casbin in the Security category based on its GitHub topics and description (tagged: "abac", "access-control", "acl"). Categories are assigned from real repository metadata, not editorial guesswork.
Read full README in the tab above.
Want a second opinion on casbin?
Ask an AI that can read this page — one click and you get its take on casbin.
 /casbin