
Threekiii/Awesome-Redteam

Threekiii/Awesome-Redteam is a open-source project on GitHub, written primarily in Python. It has 4.4k stars. 一个攻防知识库。A knowledge base for red teaming and offensive security.
Snapshot summary built from the project's own GitHub metadata — there's no written TopGit review yet. The page will update automatically when a full review is published.
TopGit writes full reviews for the most-starred, most-requested repositories. This page is a snapshot until then — see the READ ME tab for the original README in full.
Snapshot
Top contributors
Show top contributors
Awesome-Redteam
❗【免责声明】本项目所涉及的技术、思路和工具仅供学习,任何人不得将其用于非法用途和盈利,不得将其用于非授权渗透测试,否则后果自行承担,与本项目无关。 使用本项目前请先阅读 法律法规。
Disclaimer: The technologies, concepts, and tools provided in this Git repository are intended for educational and research purposes only. Any use for illegal activities, unauthorized penetration testing, or commercial purposes is strictly prohibited. Please read the Awesome-Laws before using this repository.
📖 一个攻防知识库。A knowledge base for red teaming and offensive security.
👍 means recommend 推荐使用
Roadmap
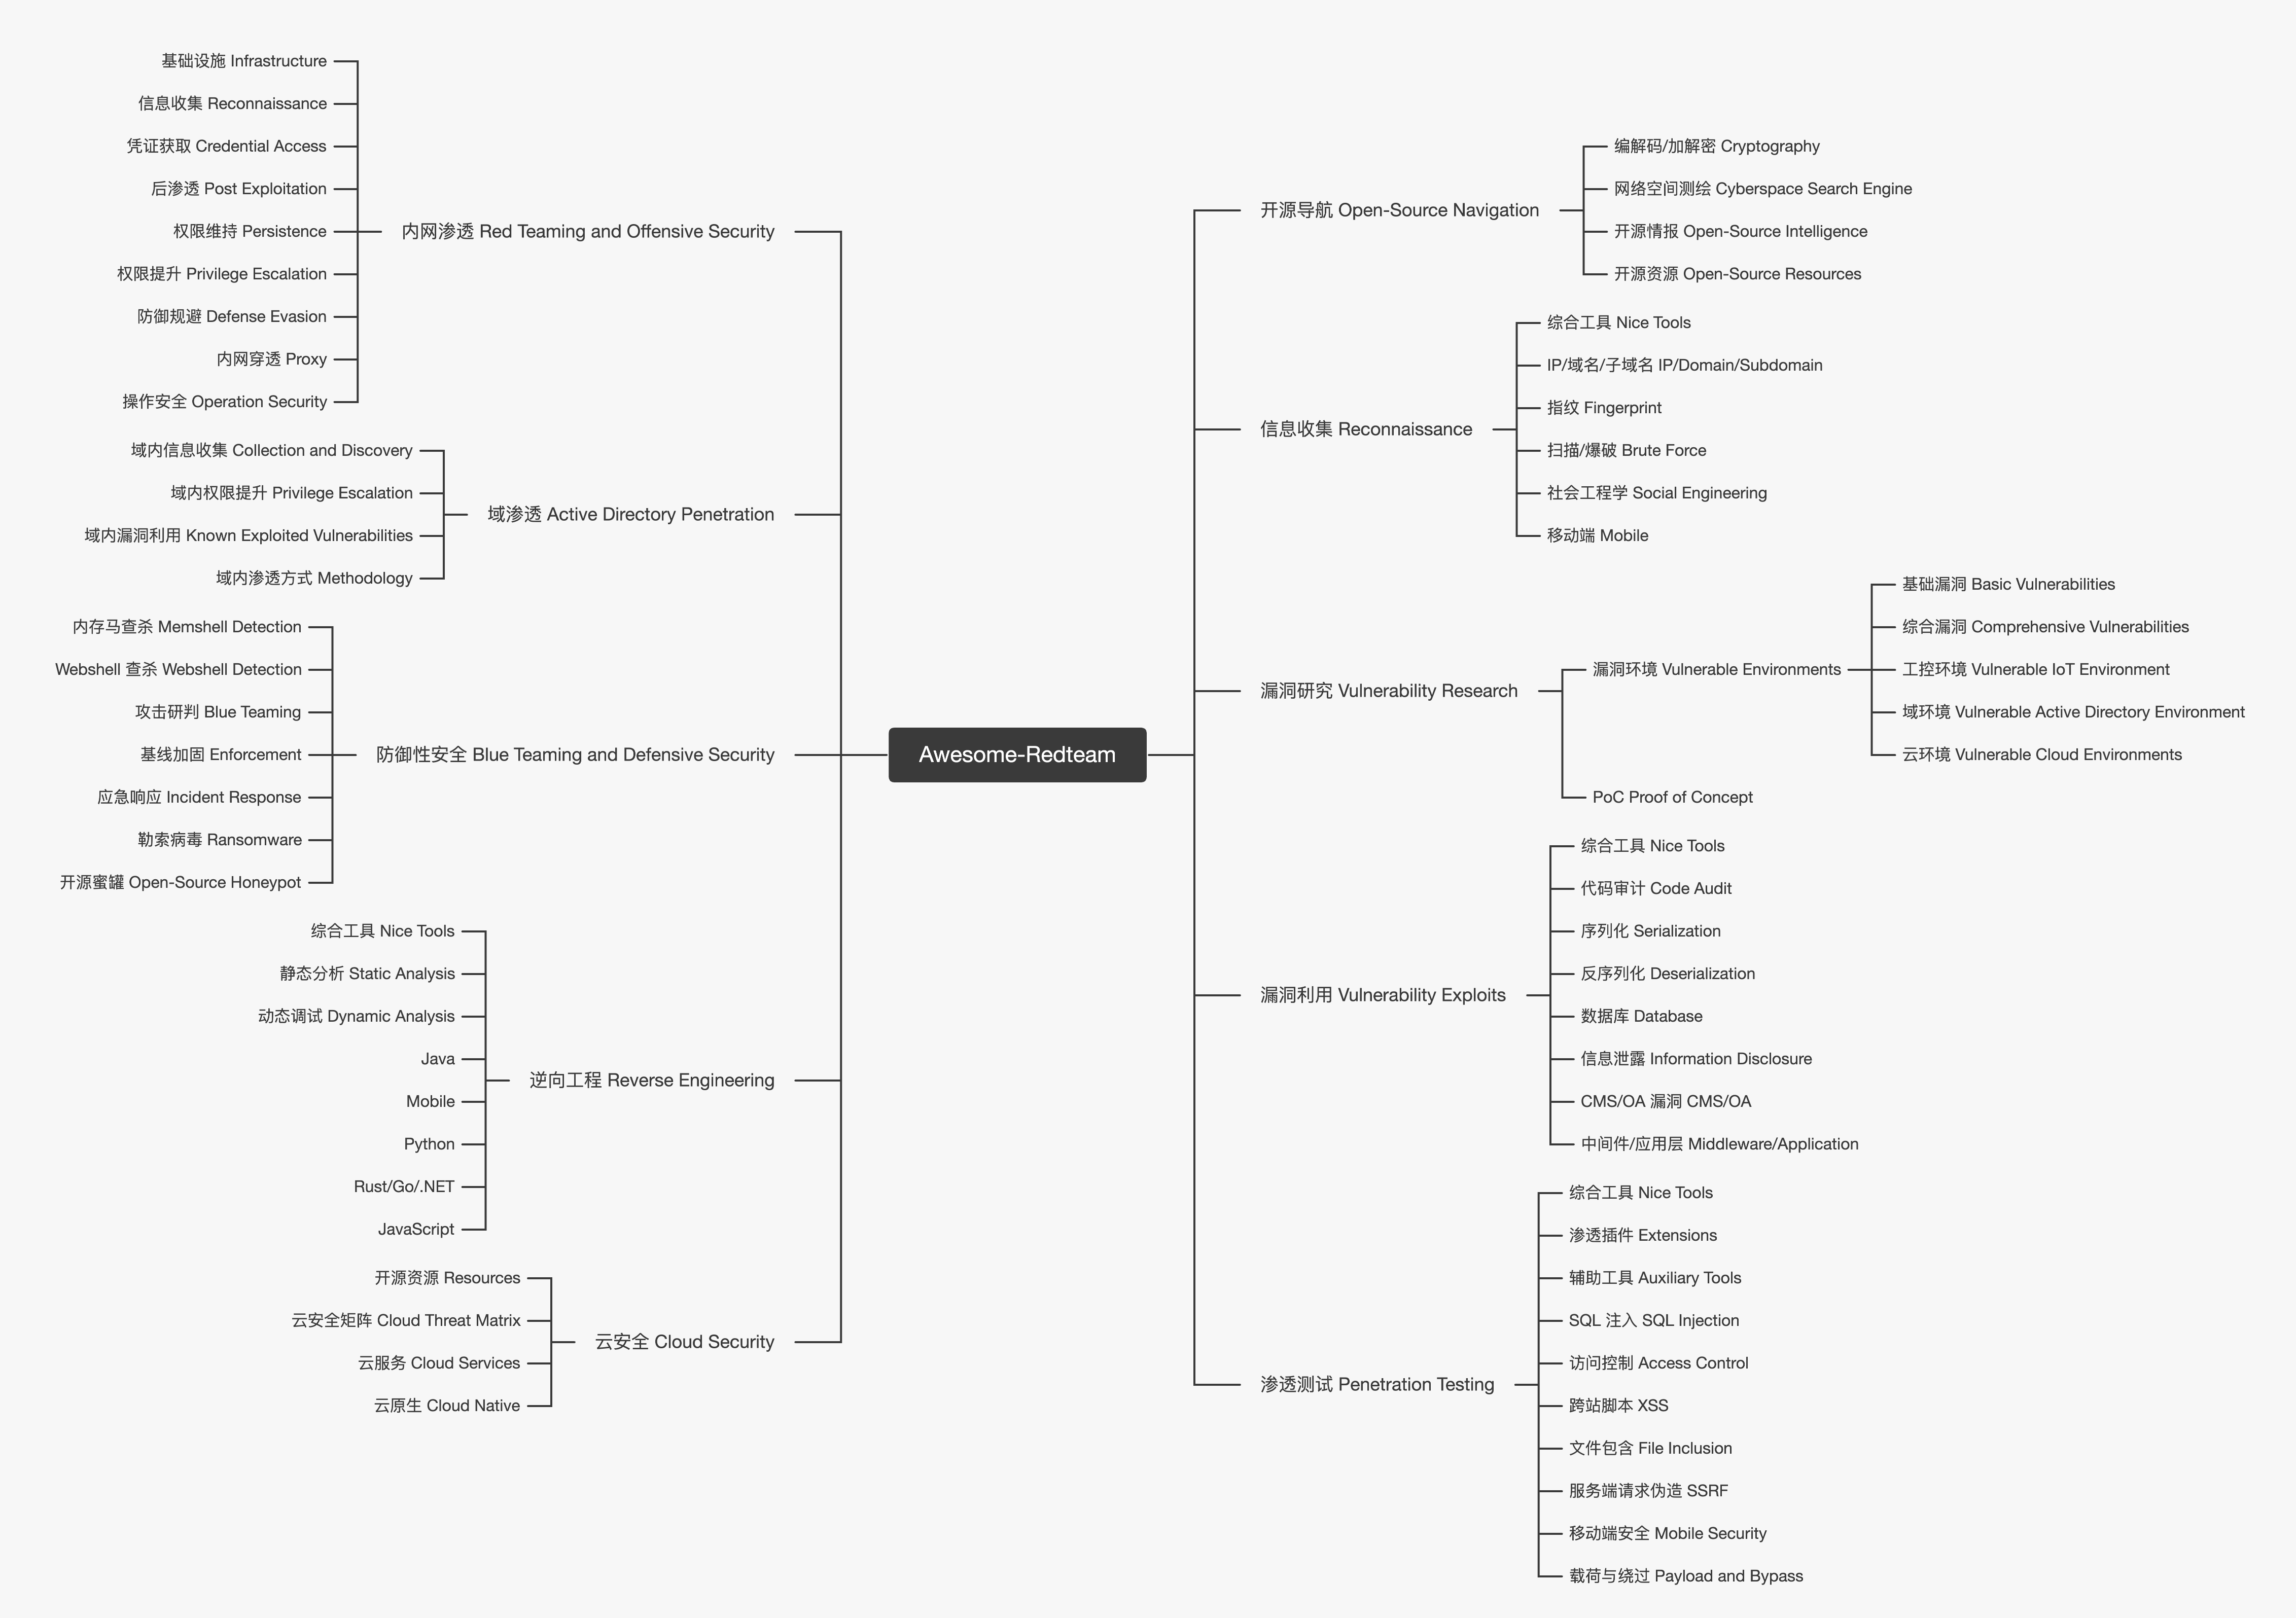
目录 Contents
- 项目导航 Project Navigation
- 速查文档 CheatSheets
- 一些代码 Scripts
- 攻防知识 Tips
- 开源导航 Open-Source Navigation
- 编解码/加解密 Cryptography
- 在线工具 Online Tools
- 离线工具 Offline Tools
- 编码/解码 Encode/Decode
- 正则表达式 Regular Expressions
- 哈希算法 Hash Algorithms
- 公钥密码算法 RSA
- 国密算法 SM Algorithms
- 网络空间测绘 Cyberspace Search Engine
- 综合工具 Nice Tools
- 网页/端口 Web/Ports
- 谷歌搜索 Google Hacking
- Github 搜索 Github Dork
- 开源情报 Open-Source Intelligence
- 综合工具 Nice Tools
- 威胁情报 Threat Intelligence
- 漏洞披露 Disclosed Vulnerabilities
- 接口检索 API Search
- 源代码检索 Source Code Search
- 开源资源 Open-Source Resources
- 社区/知识库 Communities/Knowledge Base
- 思维导图/备忘录 Mindmap/Cheat Sheets
- 进攻性安全 Red Teaming and Offensive Security
- 防御性安全 Blue Teaming and Defensive Security
- 操作安全 Operation Security
- 实战平台 Learning and Practice Platforms
- 编解码/加解密 Cryptography
- 信息收集 Reconnaissance
- 综合工具 Nice Tools
- IP/域名/子域名 IP/Domain/Subdomain
- 指纹 Fingerprint
- 指纹库 Fingerprint Collection
- 指纹识别 Fingerprint Reconnaissance
- WAF 识别 Waf Checks
- 扫描/爆破 Brute Force
- 扫描/爆破工具 Brute Force Tools
- 扫描/爆破字典 Brute Force Dictionaries
- 字典生成 Generate a Custom Dictionary
- 默认口令查询 Default Credentials
- 社会工程学 Social Engineering
- 凭据泄露 Leaked Credentials
- 邮箱 Email
- 短信 SMS Online
- 钓鱼 Phishing
- 移动端 Mobile
- 漏洞研究 Vulnerability Research
- 漏洞环境 Vulnerable Environments
- 基础漏洞 Basic Vulnerabilities
- 综合漏洞 Comprehensive Vulnerabilities
- 工控环境 Vulnerable IoT Environment
- 域环境 Vulnerable Active Directory Environment
- 云环境 Vulnerable Cloud Environments
- PoC Proof of Concept
- PoC/ExP
- PoC 模板 PoC Templates
- 漏洞环境 Vulnerable Environments
- 漏洞利用 Vulnerability Exploits
- 综合工具 Nice Tools
- 代码审计 Code Audit
- 序列化 Serialization
- Java
- 反序列化 Deserialization
- Java
- PHP
- 数据库 Database
- Redis
- MySQL
- Oracle
- MSSQL
- 信息泄露 Information Disclosure
- CMS/OA 漏洞 CMS/OA
- 中间件/应用层 Middleware/Application
- 渗透测试 Penetration Testing
- 综合工具 Nice Tools
- 渗透插件 Extensions
- Chrome
- Burp Suite
- Yakit
- 辅助工具 Auxiliary Tools
- 工具集 Open-Source Toolkit
- 带外通道 DNSLog
- 终端优化 Command Line
- 代码美化 Beautifier
- 生成器 Generator
- SQL 注入 SQL Injection
- 访问控制 Access Control
- 403 绕过 Bypass 40X errors
- 跨站脚本 XSS
- 文件包含 File Inclusion
- 服务端请求伪造 SSRF
- 移动端安全 Mobile Security
- 小程序 Mini Program
- 应用程序 APK
- SessionKey 解密 SessionKey
- 载荷与绕过 Payload and Bypass
- 内网渗透 Red Teaming and Offensive Security
- 基础设施 Infrastructure
- 信息收集 Reconnaissance
- 凭证获取 Credential Access
- 凭证转储 Credential Dumping
- 本地枚举 Local Enumeration
- 哈希破解 NTLM Cracking
- 后渗透 Post Exploitation
- 综合工具 Nice Tools
- 二进制库 Binaries and Libraries
- 权限维持 Persistence
- 内存马 MemShell
- Webshell 管理 Webshell Management
- Webshell 免杀 Webshell Bypass
- 反弹 Shell 管理 Reverse Shell Management
- 权限提升 Privilege Escalation
- Linux 本地枚举 Linux Local Enumeration
- Windows 本地枚举 Windows Local Enumeration
- Windows 提权 Windows Exploits
- Linux 提权 Linux Exploits
- 数据库提权 Database Exploits
- 防御规避 Defense Evasion
- Linux 防御规避 Linux Defense Evasion
- Windows 防御规避 Windows Defense Evasion
- 内网穿透 Proxy
- 代理客户端 Proxy Client
- 代理工具 Proxy Tools
- DNS 隧道 DNS Tunnel
- ICMP 隧道 ICMP Tunnel
- 端口转发 Port Forwarding
- 操作安全 Operation Security
- 域渗透 Active Directory Penetration
- 域内信息收集 Collection and Discovery
- 域内权限提升 Privilege Escalation
- 域内漏洞利用 Known Exploited Vulnerabilities
- MS14-068
- noPac
- Zerologon
- ProxyLogon/ProxyShell
- ProxyNotShell
- Printnightmare
- 域内渗透方式 Methodology
- Coerce and Relay
- Delegation
- ADCS
- ACLs and ACEs
- 防御性安全 Blue Teaming and Defensive Security
- 内存马查杀 Memshell Detection
- Webshell 查杀 Webshell Detection
- 攻击研判 Blue Teaming
- 基线加固 Enforcement
- 应急响应 Incident Response
- 勒索病毒 Ransomware
- 搜索引擎 Search Engine
- 解密工具 Decryption Tools
- 开源蜜罐 Open-Source Honeypot
- 逆向工程 Reverse Engineering
- 综合工具 Nice Tools
- 静态分析 Static Analysis
- 动态调试 Dynamic Analysis
- Java
- Mobile
- Python
- Rust/Go/.NET
- 云安全 Cloud Security
- 开源资源 Resources
- 云安全矩阵 Cloud Threat Matrix
- 云服务 Cloud Services
- 云管平台 Management Tools
- AK/SK 利用 AK/SK Exploit
- 云原生 Cloud Native
- 综合工具 Nice Tools
- 容器 Docker
- 集群 Kubernetes
- 提高生产力的使用姿势
- 如何快速使用 alias
- 如何优化原生终端
- 如何解决终端中文乱码
项目导航 Project Navigation
速查文档 CheatSheets
戳这里 Click Here
DefaultCreds-Cheat-Sheet.csv
Huawei-iBMC-DefaultCreds.csv
Huawei-Product-Cheat-Sheet.csv
WeakPassword-Cheat-Sheet.csv
安全厂商及官网链接速查.txt
一些代码 Scripts
戳这里 Click Here
ShellcodeWrapper: Shellcode加密
AntivirusScanner: 杀软进程检测脚本
runtime-exec-payloads.html: java.lang.Runtime.exec() Payloads生成
Ascii2Char: ASCII码和字符互相转换脚本 修改webshell文件名密码
Weakpass_Generator: 在线弱密码生成工具 汉化版
Godzilla_Decryptor: 哥斯拉流量解密
Behinder4_Key_Bruteforce: 冰蝎4密钥爆破
Flask_Session_Decryptor: Flask session注入解密
攻防知识 Tips
戳这里 Click Here
信息收集-敏感信息收集
内网渗透-免杀
内网渗透-隐藏
内网渗透-Pentesting AD Mindmap
安全架构-网络攻击与防御图谱
平台搭建-DNS Log
流量分析-CobaltStrike
流量分析-Webshell
社会工程学-钓鱼邮件主题汇总
逆向分析-微信小程序反编译
开源导航 Open-Source Navigation
编解码/加解密 Cryptography
在线工具 Online Tools
- http://www.ip33.com/
- http://www.metools.info/
- https://www.107000.com/
- http://www.hiencode.com/
- http://www.atoolbox.net/
- https://www.sojson.com/
- https://the-x.cn/
离线工具 Offline Tools
- https://github.com/wangyiwy/oktools
- https://github.com/Ciphey/Ciphey
- https://github.com/gchq/CyberChef 👍
- http://1o1o.xyz/bo_ctfcode.html
- https://github.com/guyoung/CaptfEncoder
编码/解码 Encode/Decode
- http://code.mcdvisa.com/ 标准中文电码
- https://www.compart.com/en/unicode/ 万国码
- http://web.chacuo.net/charsetuuencode UU 编码
- https://tool.chinaz.com/tools/escape.aspx 转义/反转义
- https://zh.rakko.tools/tools/21/ HTML 实体编码
正则表达式 Regular Expressions
- https://regex101.com/
- https://github.com/VincentSit/ChinaMobilePhoneNumberRegex
- https://github.com/any86/any-rule
哈希算法 Hash Algorithms
- https://www.cmd5.org/
- https://www.somd5.com/
- https://www.onlinehashcrack.com/
- https://crackstation.net/
- https://crack.sh/
- https://passwordrecovery.io/
- https://md5decrypt.net/en/Sha256/
- https://hashes.com/en/decrypt/hash
公钥密码算法 RSA
- https://www.ssleye.com/ssltool/
- https://www.lddgo.net/en/encrypt/rsa 支持 .pem 格式
国密算法 SM Algorithms
- hutool-crypto: https://github.com/dromara/hutool hutool-crypto 模块,提供对称、非对称和摘要算法封装
- GmSSL: https://github.com/guanzhi/GmSSL SM2/SM3/SM4/SM9/SSL
- gmssl-python: https://github.com/gongxian-ding/gmssl-python SM2/SM3/SM4/SM9
- SM4: https://www.toolhelper.cn/SymmetricEncryption/SM4
网络空间测绘 Cyberspace Search Engine
综合工具 Nice Tools
- Fofa: https://fofa.info/
- Shodan: https://www.shodan.io/
- ZoomEye: https://www.zoomeye.org/
- Hunter: https://hunter.qianxin.com/
- Ditecting: https://www.ditecting.com/
- Quake: https://quake.360.cn/quake/
- Censys: https://search.censys.io/
- Netlas: https://app.netlas.io/domains/
网页/端口 Web/Ports
- Wayback Machine: https://web.archive.org/ 历史网页存档
- VisualPing: https://visualping.io/ 网站变更监控
- Dark Web Exposure: https://www.immuniweb.com/darkweb/
- SG TCP/IP: https://www.speedguide.net/ports.php 端口数据库
谷歌搜索 Google Hacking
- https://www.exploit-db.com/google-hacking-database Google Hacking 数据库
- https://github.com/cipher387/Dorks-collections-list Google Hacking 数据库
- https://cxsecurity.com/dorks/ Google Hacking 数据库
- https://dorks.faisalahmed.me/ Google Hacking 在线工具
- https://pentest-tools.com/information-gathering/google-hacking Google Hacking 在线工具
- http://advangle.com/ Google Hacking 在线工具
- https://0iq.me/gip/ Google Hacking 在线工具
- https://github.com/obheda12/GitDorker Google Hacking 命令行工具
- https://github.com/six2dez/dorks_hunter Google Hacking 命令行工具
- https://github.com/Pa55w0rd/google-hacking-assistant Chrome 扩展程序
Github 搜索 Github Dork
- https://github.com/search/advanced Github Dork
- https://github.com/obheda12/GitDorker Github Dork
- https://github.com/damit5/gitdorks_go Github Dork
开源情报 Open-Source Intelligence
综合工具 Nice Tools
- OSINT Resource List: https://start.me/p/rx6Qj8/nixintel-s-osint-resource-list
- OSINT Framework: https://osintframework.com/
- OSINT Handbook: https://i-intelligence.eu/uploads/public-documents/OSINT_Handbook_2020.pdf
威胁情报 Threat Intelligence
- Virustotal: https://www.virustotal.com/
- 腾讯哈勃分析系统: https://habo.qq.com/tool/index
- 微步在线威胁情报: https://x.threatbook.com/
- 奇安信威胁情报: https://ti.qianxin.com/
- 360 威胁情报: https://ti.360.net/
- 网络安全威胁信息共享平台: https://share.anva.org.cn/web/publicity/listPhishing
- 安恒威胁情报: https://ti.dbappsecurity.com.cn/
- 火线安全平台: https://www.huoxian.cn
- 知道创宇黑客新闻流: https://hackernews.cc/
- SecWiki 安全信息流: https://www.sec-wiki.com/
漏洞披露 Disclosed Vulnerabilities
- 国家信息安全漏洞库: https://www.cnnvd.org.cn/
- 国家互联网应急中心: https://www.cert.org.cn/
- 360 网络安全响应中心: https://cert.360.cn/
- 知道创宇漏洞库: https://www.seebug.org/
- 长亭漏洞库: https://stack.chaitin.com/vuldb/
- 阿里云漏洞库: https://avd.aliyun.com/high-risk/list
- PeiQi 漏洞库: https://peiqi.wgpsec.org/
- Hackerone: https://www.hackerone.com/
- CVE: https://cve.mitre.org/
- National Vulnerability Database: https://nvd.nist.gov/
- Vulnerability & Exploit Database: https://www.rapid7.com/db/
- Packet Storm's file archive: https://packetstormsecurity.com/files/tags/exploit
- Shodan: https://cvedb.shodan.io/cves 实时更新 CVE 漏洞信息
curl https://cvedb.shodan.io/cves | jq '[.cves[] | select(.cvss > 8)]' - CVEShield: https://www.cveshield.com/ 最新热门漏洞
接口检索 API Search
- https://www.postman.com/explore/ 公共 API
- https://rapidapi.com/ 公共 API
- https://serene-agnesi-57a014.netlify.app/ 发现 API keys
源代码检索 Source Code Search
- https://publicwww.com/
- https://searchcode.com/
开源资源 Open-Source Resources
社区/知识库 Communities/Knowledge Base
- 先知社区: https://xz.aliyun.com/
- Infocon: https://infocon.org/
- ffffffff0x 安全知识框架: https://github.com/ffffffff0x/1earn
- 狼组公开知识库: https://wiki.wgpsec.org/
- Mitre ATT&CK matrices: https://attack.mitre.org/matrices/enterprise
- Mitre ATT&CK techniques: http://attack.mitre.org/techniques/enterprise/
- Hacking Articles: https://www.hackingarticles.in/
- PostSwigger Blog: https://portswigger.net/blog
- InGuardians Labs Blog: https://www.inguardians.com/
- Pentest Workflow: https://pentest.mxhx.org/
- Pentest Cheatsheet: https://pentestbook.six2dez.com/
思维导图/备忘录 Mindmap/Cheat Sheets
- https://cheatsheets.zip/ 开发者速查表
- https://learnxinyminutes.com/ 编程/工具/命令/操作系统/快捷键速查表
- https://github.com/Ignitetechnologies/Mindmap/ 网络安全思维导图
- https://html5sec.org/ HTML5 安全速查表
- https://orange-cyberdefense.github.io/ocd-mindmaps/img/mindmap_ad_dark_classic_2025.03.excalidraw.svg 域攻防思维导图
- https://github.com/WADComs/WADComs.github.io Windows/域速查表 👍
进攻性安全 Red Teaming and Offensive Security
- https://www.ired.team/
- https://www.thehacker.recipes/
- https://ppn.snovvcrash.rocks/
- https://book.hacktricks.xyz/
- https://blog.harmj0y.net/
- https://hausec.com/domain-penetration-testing/
- https://dirkjanm.io/
- https://casvancooten.com/
- https://evasions.checkpoint.com/
- https://redteam.guide/docs/definitions
- https://github.com/HadessCS/Red-team-Interview-Questions
防御性安全 Blue Teaming and Defensive Security
- https://github.com/Purp1eW0lf/Blue-Team-Notes
操作安全 Operation Security
- https://github.com/WesleyWong420/OPSEC-Tradecraft
实战平台 Learning and Practice Platforms
- Cybrary: https://www.cybrary.it/
- HacktheBox: https://www.hackthebox.com/
- TryHackMe: https://tryhackme.com/
- Try2Hack: https://try2hack.me/
- Vulnmachines: https://www.vulnmachines.com/
- RangeForce: https://www.rangeforce.com/
- Root Me: https://www.root-me.org/
- ichunqiu: https://yunjing.ichunqiu.com/
- echoCTF: https://github.com/echoCTF/echoCTF.RED 适用于 CTF 竞赛
- Vulnhub: https://www.vulnhub.com/
Mac M1 使用 Vulnhub 等 ova 格式镜像,需要将 ova 格式转为 qcow2,再通过 UTM 运行:
- https://github.com/qemu/qemu
- https://github.com/utmapp/UTM
信息收集 Reconnaissance
综合工具 Nice Tools
- AlliN: https://github.com/P1-Team/AlliN
- fscan: https://github.com/shadow1ng/fscan
- qscan: https://github.com/qi4L/qscan
- TscanPlus: https://github.com/TideSec/TscanPlus
- dddd: https://github.com/SleepingBag945/dddd
- kscan: https://github.com/lcvvvv/kscan
- Kunyu: https://github.com/knownsec/Kunyu
- OneForAll: https://github.com/shmilylty/OneForAll
- ShuiZe: https://github.com/0x727/ShuiZe_0x727
- FofaX: https://github.com/xiecat/fofax
- Fofa Viewer: https://github.com/wgpsec/fofa_viewer
- ENScan_GO: https://github.com/wgpsec/ENScan_GO
- Amass: https://github.com/owasp-amass/amass
- ApolloScanner: https://github.com/b0bac/ApolloScanner
IP/域名/子域名 IP/Domain/Subdomain
- IP:
- https://www.ipuu.net/
- https://site.ip138.com/
- https://myip.ms/
- https://ipwhois.cnnic.net.cn
- Multi Ping:
- https://ping.chinaz.com/
- https://www.host-tracker.com/
- https://www.webpagetest.org/
- https://dnscheck.pingdom.com/
- IP to Domain:
- https://site.ip138.com/
- https://x.threatbook.cn/
- https://www.virustotal.com/
- Whois:
- https://whois.chinaz.com/
- https://whois.aliyun.com/
- https://who.is/
- https://www.whoxy.com/
- DNS:
- https://hackertarget.com/find-dns-host-records
- https://dnsdumpster.com
- https://dnsdb.io/zh-cn
- https://centralops.net/co/
- https://viewdns.info/
- https://dnsdumpster.com/
- https://rapiddns.io/
- ASN:
- https://wq.apnic.net/
- https://bgp.he.net/
- https://bgpview.io/
- TLS/SSL 证书:
- https://censys.io
- https://crt.sh
指纹 Fingerprint
指纹库 Fingerprint Collection
- https://github.com/r0eXpeR/fingerprint
- https://github.com/0x727/FingerprintHub
指纹识别 Fingerprint Reconnaissance
- https://github.com/EASY233/Finger
- https://github.com/EdgeSecurityTeam/EHole
- https://github.com/lemonlove7/EHole_magic
- https://github.com/0x727/ObserverWard
- https://github.com/TideSec/TideFinger_Go
- https://github.com/zhzyker/dismap
- https://www.webshell.cc/4697.html
- http://www.yunsee.cn/ online
WAF 识别 Waf Checks
- https://github.com/stamparm/identYwaf
- https://github.com/EnableSecurity/wafw00f
- https://github.com/MISP/misp-warninglists
扫描/爆破 Brute Force
扫描/爆破工具 Brute Force Tools
- Port:
- https://github.com/antirez/hping
- Subdomain:
- https://github.com/projectdiscovery/subfinder
- https://github.com/knownsec/ksubdomain
- Web:
- https://github.com/pingc0y/URLFinder
- https://github.com/s0md3v/Arjun
- https://github.com/OJ/gobuster
- https://github.com/jaeles-project/gospider
- https://github.com/xmendez/wfuzz
- Directory:
- https://github.com/maurosoria/dirsearch
- https://github.com/H4ckForJob/dirmap
- https://github.com/ffuf/ffuf
- Password:
- https://github.com/vanhauser-thc/thc-hydra
- https://github.com/galkan/crowbar 支持 sshkey 和 openvpn
- https://github.com/evilsocket/legba/
- Hash 破解:
- https://github.com/openwall/john
- https://github.com/hashcat/hashcat
- https://hashcat.net/wiki/doku.php?id=example_hashes hashcat 示例
- https://github.com/HashPals/Name-That-Hash 哈希类型识别
- https://github.com/noraj/haiti 哈希类型识别
- Json web token (JWT):
- https://jwt.io/
- https://github.com/Sjord/jwtcrack
- https://github.com/ticarpi/jwt_tool
- https://github.com/mazen160/jwt-pwn
- https://github.com/brendan-rius/c-jwt-cracker
- https://github.com/wallarm/jwt-secrets/blob/master/jwt.secrets.list
- https://github.com/hahwul/jwt-hack
扫描/爆破字典 Brute Force Dictionaries
- Wordlists for All:
- https://github.com/danielmiessler/SecLists 46.4k star
- https://github.com/SexyBeast233/SecDictionary + ffuf
- https://github.com/insightglacier/Dictionary-Of-Pentesting
- https://github.com/TheKingOfDuck/fuzzDicts
- https://github.com/gh0stkey/Web-Fuzzing-Box
- https://github.com/a3vilc0de/PentesterSpecialDict
- https://github.com/Bo0oM/fuzz.txt
- https://github.com/assetnote/wordlists
- https://github.com/rapid7/metasploit-framework/tree/master/data/wordlists
- Web Fuzz Wordlists:
- https://github.com/xmendez/wfuzz/tree/master/wordlist
- https://github.com/lutfumertceylan/top25-parameter
- Others (not frequently used):
- https://github.com/danielmiessler/SecLists/tree/master/Discovery/Web-Content
- https://github.com/assetnote/commonspeak2-wordlists/tree/master/wordswithext
- https://github.com/random-robbie/bruteforce-lists
- https://github.com/google/fuzzing/tree/master/dictionaries
- https://github.com/six2dez/OneListForAll
字典生成 Generate a Custom Dictionary
- Online:
- Generate wordlists: https://weakpass.com/generate
- Generate subdomains and wordlists: https://weakpass.com/generate/domains
- 汉字转拼音: https://www.aies.cn/pinyin.htm
- 密码猜解: https://www.hacked.com.cn/pass.html
- Private Deployment:
- Generate wordlists(offline): https://github.com/zzzteph/weakpass
- Generate subdomains and wordlists(offline): https://github.com/zzzteph/probable_subdomains
- Offline:
- pydictor: https://github.com/LandGrey/pydictor/
- crunch:
- Kali/Linux: https://sourceforge.net/projects/crunch-wordlist
- Windows: https://github.com/shadwork/Windows-Crunch
默认口令查询 Default Credentials
- Default Credentials Cheat Sheet: https://github.com/ihebski/DefaultCreds-cheat-sheet 3468 条默认口令
- datarecovery: https://datarecovery.com/rd/default-passwords/ online
- cirt.net: https://cirt.net/passwords online
- Online Router Passwords:
- https://www.routerpasswords.com/
- https://portforward.com/router-password/
- https://www.cleancss.com/router-default/
- https://www.toolmao.com/baiduapp/routerpwd/
- https://datarecovery.com/rd/default-passwords/
社会工程学 Social Engineering
凭据泄露 Leaked Credentials
- https://have-ibeenpwned.com/
- https://breachdirectory.org/
邮箱 Email
- Temporary Email:
- http://24mail.chacuo.net/
- https://www.guerrillamail.com/
- https://rootsh.com/
- Snov.io: https://app.snov.io
- Phonebook: 同时支持子域名和 URL https://phonebook.cz
- Skymem: https://www.skymem.info
- Hunter: https://hunter.io
- email-format: https://www.email-format.com/i/search/
- 搜邮箱: https://souyouxiang.com/find-contact/
- theHarvester: 同时支持子域名查询 https://github.com/laramies/theHarvester
- Verify emails: https://tools.emailhippo.com/
- Accounts registered by email: https://emailrep.io/
短信 SMS Online
- https://sms-activate.io 👍 覆盖 180+ 国家
- https://www.supercloudsms.com/en/
- https://getfreesmsnumber.com/
- https://www.zusms.com/
- https://yunduanxin.net/
- https://www.free-sms-receive.com/
- https://receive-sms.cc/#google_vignette
- https://bestsms.xyz/
- https://smscodeonline.com/
钓鱼 Phishing
- gophish: https://github.com/gophish/gophish 开源钓鱼工具包
- SpoofWeb: https://github.com/5icorgi/SpoofWeb 部署钓鱼网站
移动端 Mobile
- https://www.xiaolanben.com/
- https://www.qimai.cn/
漏洞研究 Vulnerability Research
漏洞环境 Vulnerable Environments
基础漏洞 Basic Vulnerabilities
- Sqli-labs: https://github.com/Audi-1/sqli-labs
- Upload-labs: https://github.com/c0ny1/upload-labs
- Xss-labs: https://github.com/do0dl3/xss-labs
- DVWA: https://github.com/digininja/DVWA
- WebGoat: https://github.com/WebGoat/WebGoat
- encrypt-labs: https://github.com/SwagXz/encrypt-labs AES/DES/RSA
综合漏洞 Comprehensive Vulnerabilities
- Vulhub: https://vulhub.org/
- PortSwigger Web Security Academy: https://portswigger.net/web-security
- OWASP Top10: https://owasp.org/www-project-juice-shop/
- Vulstudy: https://github.com/c0ny1/vulstudy 基于 Docker 的 17 个漏洞平台
- Vulfocus: https://github.com/fofapro/vulfocus
- FastJsonParty: https://github.com/lemono0/FastJsonParty
工控环境 Vulnerable IoT Environment
- IoT-vulhub: https://github.com/firmianay/IoT-vulhub
域环境 Vulnerable Active Directory Environment
- Game of active directory: https://github.com/Orange-Cyberdefense/GOAD
- BadBlood: https://github.com/davidprowe/BadBlood 创建你自己的示例 Active Directory 环境
云环境 Vulnerable Cloud Environments
- Awesome-CloudSec-Labs: https://github.com/iknowjason/Awesome-CloudSec-Labs
- K8s Lan Party: https://www.k8slanparty.com/
- badPods: https://github.com/BishopFox/badPods
- Metarget: https://github.com/Metarget/metarget
- TerraformGoat: https://github.com/HXSecurity/TerraformGoat
- Kubernetes Goat: https://github.com/madhuakula/kubernetes-goat
- Attack Defense: https://attackdefense.pentesteracademy.com/listing?labtype=cloud-services&subtype=cloud-services-amazon-s3
- AWSGoat: https://github.com/ine-labs/AWSGoat
- CloudGoat: https://github.com/RhinoSecurityLabs/cloudgoat
PoC Proof of Concept
Be careful Malware,POC 库最新的 CVE 可能存在投毒风险。
PoC/ExP
- https://github.com/wy876/POC
- https://github.com/lal0ne/vulnerability
- https://github.com/DawnFlame/POChouse
- https://github.com/coffeehb/Some-PoC-oR-ExP
- https://github.com/luck-ying/Library-POC
- https://github.com/Mr-xn/Penetration_Testing_POC
- https://github.com/nomi-sec/PoC-in-GitHub
- https://github.com/ycdxsb/PocOrExp_in_Github
- https://github.com/helloexp/0day
- https://github.com/trickest/cve
- https://sploitus.com/ 本周漏洞利用集合
- https://www.exploit-db.com/ 配合
searchsploit <关键词>使用
PoC 模板 PoC Templates
- https://poc.xray.cool/
- https://github.com/zeoxisca/gamma-gui online
- https://github.com/projectdiscovery/nuclei-templates/ offline
漏洞利用 Vulnerability Exploits
综合工具 Nice Tools
- https://github.com/chaitin/xpoc
- https://github.com/chaitin/xray
- https://github.com/zhzyker/vulmap
- https://github.com/zan8in/afrog
- https://github.com/projectdiscovery/nuclei
代码审计 Code Audit
- tabby: https://github.com/wh1t3p1g/tabby
序列化 Serialization
Java
- https://github.com/phith0n/zkar
反序列化 Deserialization
Java
- https://github.com/frohoff/ysoserial
- https://github.com/Y4er/ysoserial
- https://github.com/wh1t3p1g/ysomap
- https://github.com/mbechler/marshalsec
- https://github.com/qi4L/JYso
- https://github.com/vulhub/JNDIExploit
- https://github.com/welk1n/JNDI-Injection-Exploit
- https://github.com/WhiteHSBG/JNDIExploit
- https://github.com/rebeyond/JNDInjector
- https://github.com/A-D-Team/attackRmi
- https://github.com/Java-Chains/web-chains
- https://github.com/DeEpinGh0st/ysoserial
PHP
- https://github.com/ambionics/phpggc PHP 反序列化漏洞利用载荷
数据库 Database
Redis
- https://github.com/cinience/RedisStudio
- https://github.com/qishibo/AnotherRedisDesktopManager
- https://github.com/n0b0dyCN/redis-rogue-server
- https://github.com/Ridter/redis-rce
- https://github.com/yuyan-sec/RedisEXP
- https://github.com/r35tart/RedisWriteFile
MySQL
- https://github.com/SafeGroceryStore/MDUT 多数据库利用工具
- https://github.com/4ra1n/mysql-fake-server
- https://github.com/dushixiang/evil-mysql-server
- https://github.com/fnmsd/MySQL_Fake_Server
Oracle
- odat: https://github.com/quentinhardy/odat 远程代码执行
- sqlplus: https://www.oracle.com/database/technologies/instant-client/linux-x86-64-downloads.html 以 sysdba 身份执行
MSSQL
- https://github.com/uknowsec/SharpSQLTools
- https://github.com/Ridter/PySQLTools
信息泄露 Information Disclosure
- trufflehog: https://github.com/trufflesecurity/trufflehog 发现、验证并分析泄露的凭据
- git-dumper: https://github.com/arthaud/git-dumper
- gitleaks: https://github.com/gitleaks/gitleaks
- dvcs-ripper: https://github.com/kost/dvcs-ripper .svn、.hg、.cvs 信息泄露
- ds_store_exp: https://github.com/lijiejie/ds_store_exp .DS_Store 信息泄露
- Hawkeye: https://github.com/0xbug/Hawkeye GitHub 敏感信息泄露监控爬虫
CMS/OA 漏洞 CMS/OA
- TongdaScan_go: https://github.com/Fu5r0dah/TongdaScan_go
- Apt_t00ls: https://github.com/White-hua/Apt_t00ls
- OA-EXPTOOL: https://github.com/LittleBear4/OA-EXPTOOL
- DecryptTools: https://github.com/wafinfo/DecryptTools 22 种加解密
- ncDecode: https://github.com/1amfine2333/ncDecode 用友 NC 解密
- PassDecode-jar: https://github.com/Rvn0xsy/PassDecode-jar 帆软/致远解密
- ezOFFICE_Decrypt: https://github.com/wafinfo/ezOFFICE_Decrypt 万户解密
- LandrayDES: https://github.com/zhutougg/LandrayDES 蓝凌 OA 解密
中间件/应用层 Middleware/Application
Confluence
- ConfluenceMemshell: https://github.com/Lotus6/ConfluenceMemshell
- CVE-2022-26134 Memshell: https://github.com/BeichenDream/CVE-2022-26134-Godzilla-MEMSHELL
- CVE-2023-22527 Memshell: https://github.com/Boogipop/CVE-2023-22527-Godzilla-MEMSHELL
Druid
- DruidCrack: https://github.com/rabbitmask/DruidCrack
- druid_sessions: https://github.com/yuyan-sec/druid_sessions
Fastjson
- fastjson-exp: https://github.com/amaz1ngday/fastjson-exp
GitLab
- CVE-2021-22205: https://github.com/Al1ex/CVE-2021-22205/
Nacos
- NacosRce: https://github.com/c0olw/NacosRce/
- nacosleak: https://github.com/a1phaboy/nacosleak
- nacosScan: https://github.com/Whoopsunix/nacosScan
- NacosExploitGUI: https://github.com/charonlight/NacosExploitGUI
Nps
- nps-auth-bypass: https://github.com/carr0t2/nps-auth-bypass
Java
- jdwp-shellifier: python2 https://github.com/IOActive/jdwp-shellifier
- jdwp-shellifier: https://github.com/Lz1y/jdwp-shellifier
- jascypt encryption & decryption: https://www.devglan.com/online-tools/jasypt-online-encryption-decryption Jasypt 加解密工具
Shiro
- Shiro rememberMe Decrypt: https://vulsee.com/tools/shiroDe/shiroDecrypt.html
- shiro_attack: https://github.com/j1anFen/shiro_attack
- shiro_rce_tool: https://github.com/wyzxxz/shiro_rce_tool
- ShiroExploit: https://github.com/feihong-cs/ShiroExploit-Deprecated
- ShiroExp: https://github.com/safe6Sec/ShiroExp
- shiro_key: https://github.com/yanm1e/shiro_key 1000+ key
Struts
- Struts2VulsTools: https://github.com/shack2/Struts2VulsTools
Spring Boot
- SpringBoot-Scan: https://github.com/AabyssZG/SpringBoot-Scan
- SpringBootVulExploit: https://github.com/LandGrey/SpringBootVulExploit
- CVE-2022-22963 https://github.com/mamba-2021/EXP-POC/tree/main/Spring-cloud-function-SpEL-RCE
- CVE-2022-22947/CVE-2022-22963: https://github.com/savior-only/Spring_All_Reachable
- swagger-exp: https://github.com/lijiejie/swagger-exp
- heapdump_tool: https://github.com/wyzxxz/heapdump_tool
- Memory Analyzer: https://eclipse.dev/mat/download/
- JDumpSpider: https://github.com/whwlsfb/JDumpSpider
Tomcat
- CVE-2020-1938: https://github.com/YDHCUI/CNVD-2020-10487-Tomcat-Ajp-lfi
- ClassHound: https://github.com/LandGrey/ClassHound
Thinkphp
- ThinkphpGUI: https://github.com/Lotus6/ThinkphpGUI
- thinkphp_gui_tools: https://github.com/bewhale/thinkphp_gui_tools
Weblogic
- WeblogicTool: https://github.com/KimJun1010/WeblogicTool
- WeblogicScan: https://github.com/dr0op/WeblogicScan
- WeblogicScan: https://github.com/rabbitmask/WeblogicScan
- weblogicScanner: https://github.com/0xn0ne/weblogicScanner
- weblogic-framework: https://github.com/sv3nbeast/weblogic-framework
- CVE-2020-14882: https://github.com/zhzyker/exphub/blob/master/weblogic/cve-2020-14882_rce.py
WebSocket
- wscat: https://github.com/websockets/wscat
vCenter
- VcenterKiller: https://github.com/Schira4396/VcenterKiller
- VcenterKit: https://github.com/W01fh4cker/VcenterKit
- vcenter_saml_login: https://github.com/horizon3ai/vcenter_saml_login 提取身份提供商(IdP)证书
Zookeeper
- ZooInspector: https://issues.apache.org/jira/secure/attachment/12436620/ZooInspector.zip
- apache-zookeeper: https://archive.apache.org/dist/zookeeper/zookeeper-3.5.6/ zkCli.sh 命令行工具
渗透测试 Penetration Testing
综合工具 Nice Tools
- Yakit: https://github.com/yaklang/yakit
- Burpsuite: https://portswigger.net/burp
渗透插件 Extensions
Chrome
- ZeroOmega: https://github.com/zero-peak/ZeroOmega 适配 manifest v3 的 proxy switchyOmega
- serp-analyzer: https://leadscloud.github.io/serp-analyzer/ 显示域名/IP
- FindSomething: https://github.com/ResidualLaugh/FindSomething 在源代码或 javascript 中查找内容
- Hack Bar: https://github.com/0140454/hackbar
- Wappalyzer: https://www.wappalyzer.com/ 识别网站使用的技术栈
- EditThisCookie: https://www.editthiscookie.com/
- Cookie-Editor: https://github.com/Moustachauve/cookie-editor
- Disable JavaScript: https://github.com/dpacassi/disable-javascript
- Heimdallr: https://github.com/Ghr07h/Heimdallr 蜜罐检测工具
- anti-honeypot:https://github.com/cnrstar/anti-honeypot 蜜罐检测工具
- immersive-translate: https://github.com/immersive-translate/immersive-translate/ 翻译工具
- relingo: https://cn.relingo.net/en/ 翻译工具
- json-formatter: https://github.com/callumlocke/json-formatter
- markdown-viewer: https://github.com/simov/markdown-viewer
Burp Suite
- HaE: https://github.com/gh0stkey/HaE 高亮和提取工具
- Log4j2Scan: https://github.com/whwlsfb/Log4j2Scan Log4j 漏洞扫描工具
- RouteVulScan: https://github.com/F6JO/RouteVulScan 路由漏洞扫描工具
- BurpCrypto: https://github.com/whwlsfb/BurpCrypto 支持 AES/RSA/DES/ExecJs 加密解密
- domain hunter: https://github.com/bit4woo/domain_hunter_pro 域名收集工具
- BurpAppletPentester: https://github.com/mrknow001/BurpAppletPentester sessionkey 解密工具
- autoDecoder: https://github.com/f0ng/autoDecoder 加解密
Yakit
- HaeToYakit: https://github.com/youmulijiang/HaeToYakit
辅助工具 Auxiliary Tools
工具集 Open-Source Toolkit
- https://forum.ywhack.com/bountytips.php?tools
- https://github.com/knownsec/404StarLink
- https://pentest-tools.com/
带外通道 DNSLog
- dig.pm: https://dig.pm/
- ceye.io: http://ceye.io/
- dnslog.cn: http://dnslog.cn/
- Alphalog: dns/http/rmi/ldap https://github.com/AlphabugX/Alphalog
- DNS rebinding: https://lock.cmpxchg8b.com/rebinder.html
- DNSLog-GO: https://github.com/lanyi1998/DNSlog-GO
终端优化 Command Line
- https://github.com/ohmyzsh/ohmyzsh zsh 命令行增强工具
- https://github.com/chrisant996/clink cmd.exe 命令行增强工具
- https://github.com/hanslub42/rlwrap readline 包装器
- https://github.com/Eugeny/tabby 适用于 Windows 的终端工具
- https://github.com/warpdotdev/Warp 适用于 Mac 的终端工具
- https://github.com/zellij-org/zellij 终端复用器
- https://github.com/tmux 终端复用器
- https://github.com/tomnomnom/anew 向文件添加新行并跳过重复项的工具
- https://github.com/jlevy/the-art-of-command-line
- Linux command line:
- https://github.com/jaywcjlove/linux-command 在线查询工具
- https://github.com/chenjiandongx/pls go 版本
- https://github.com/chenjiandongx/how python 版本
- https://explainshell.com/ 解释 shell 命令含义
- https://github.com/BurntSushi/ripgrep 面向行的搜索工具(速度更快)
代码美化 Beautifier
- http://web.chacuo.net/formatsh
- https://beautifier.io/
- http://jsnice.org/
生成器 Generator
- revshells: https://www.revshells.com/
- reverse-shell: https://forum.ywhack.com/reverse-shell/
- reverse-shell-generator: https://tex2e.github.io/reverse-shell-generator/index.html
- reverse-shell-generator: https://github.com/0dayCTF/reverse-shell-generator
- File-Download-Generator: https://github.com/r0eXpeR/File-Download-Generator
SQL 注入 SQL Injection
- https://github.com/sqlmapproject/sqlmap
- https://github.com/payloadbox/sql-injection-payload-list
访问控制 Access Control
403 绕过 Bypass 40X errors
- https://github.com/yunemse48/403bypasser
- https://github.com/lobuhi/byp4xx
- https://github.com/Dheerajmadhukar/4-ZERO-3
- https://github.com/devploit/nomore403
跨站脚本 XSS
- XSS Chop: https://xsschop.chaitin.cn/demo/
- XSS/CSRF: https://evilcos.me/lab/xssor/
文件包含 File Inclusion
- https://github.com/hansmach1ne/lfimap
- https://github.com/mzfr/liffy
服务端请求伪造 SSRF
- https://portswigger.net/web-security/ssrf/url-validation-bypass-cheat-sheet
- https://github.com/tarunkant/Gopherus 适用于 py2 的 Gopherus 工具
- https://github.com/Esonhugh/Gopherus3 适用于 py3 的 Gopherus 工具
移动端安全 Mobile Security
小程序 Mini Program
[wxappUnpacker: https://github.com/xuedingmiaojun/wxappUnpacker]- https://github.com/Cherrison/CrackMinApp
- https://github.com/mrknow001/API-Explorer ak/sk 获取工具
- https://github.com/eeeeeeeeee-code/e0e1-wx
- https://github.com/wux1an/wxapkg
应用程序 APK
- https://github.com/kelvinBen/AppInfoScanner
- https://github.com/iBotPeaches/Apktool
SessionKey 解密 SessionKey
- https://github.com/mrknow001/wx_sessionkey_decrypt
载荷与绕过 Payload and Bypass
- PayloadsAllTheThings: https://github.com/swisskyrepo/PayloadsAllTheThings
- IP to Decimal: https://www.browserling.com/tools/ip-to-dec IP 转十进制(127.0.0.1 >>> 2130706433)
- java.lang.Runtime.exec() Payload: https://payloads.net/Runtime.exec/
- PHPFuck: https://github.com/splitline/PHPFuck
- JSFuck: http://www.jsfuck.com/
- JavaScript Deobfuscator and Unpacker: https://lelinhtinh.github.io/de4js/ JavaScript 反混淆和解包工具
- CVE-2021-44228-PoC-log4j-bypass-words: https://github.com/Puliczek/CVE-2021-44228-PoC-log4j-bypass-words
内网渗透 Red Teaming and Offensive Security
基础设施 Infrastructure
- f8x: https://github.com/ffffffff0x/f8x 红队/蓝队环境自动化部署工具
- openvpn-install: https://github.com/hwdsl2/openvpn-install OpenVPN 服务器安装脚本
- cloudreve: https://github.com/cloudreve/Cloudreve 支持多云的自建文件管理系统
- updog: https://github.com/sc0tfree/updog 通过 HTTP/S 上传下载文件
- mattermost: https://github.com/mattermost/mattermost
- rocketchat: https://github.com/RocketChat/Rocket.Chat
- codimd: https://github.com/hackmdio/codimd
- hedgedoc: https://github.com/hedgedoc/hedgedoc
信息收集 Reconnaissance
- SharpHunter: https://github.com/lintstar/SharpHunter 自动化主机信息搜集工具
- netspy: https://github.com/shmilylty/netspy 内网网段探测
- SharpHostInfo: https://github.com/shmilylty/SharpHostInfo
- SharpScan: https://github.com/INotGreen/SharpScan
- smbmap: https://github.com/ShawnDEvans/smbmap SMB 枚举
凭证获取 Credential Access
凭证转储 Credential Dumping
- LaZagne: https://github.com/AlessandroZ/LaZagne
- WirelessKeyView: https://www.nirsoft.net/utils/wireless_key.html
- Windows credential manager: https://www.nirsoft.net/utils/credentials_file_view.html
- Pillager: https://github.com/qwqdanchun/Pillager/
- searchall: https://github.com/Naturehi666/searchall
- pypykatz: https://github.com/skelsec/pypykatz 纯 Python 实现的 mimikatz
- regsecrets & dpapidump: https://github.com/fortra/impacket/pull/1898 已在 Windows 11 和 Server 2022 测试无问题
- DonPAPI: https://github.com/login-securite/DonPAPI
- SharpDPAPI: https://github.com/GhostPack/SharpDPAPI
- dploot: https://github.com/zblurx/dploot DPAPI
- PPLdump: https://github.com/itm4n/PPLdump 受保护进程 LSASS 读取
- lsassy: https://github.com/login-securite/lsassy
本地枚举 Local Enumeration
- HackBrowserData: https://github.com/moonD4rk/HackBrowserData
- BrowserGhost: https://github.com/QAX-A-Team/BrowserGhost
- chrome: http://www.nirsoft.net/utils/chromepass.html
- firefox: https://github.com/unode/firefox_decrypt
- foxmail: https://securityxploded.com/foxmail-password-decryptor.php
- mobaxterm: https://github.com/HyperSine/how-does-MobaXterm-encrypt-password
- navicat: https://github.com/Zhuoyuan1/navicat_password_decrypt
- navicat: https://github.com/HyperSine/how-does-navicat-encrypt-password
- sunflower: https://github.com/wafinfo/Sunflower_get_Password
- FindToDeskPass: https://github.com/yangliukk/FindToDeskPass
- sundeskQ: sunflower & todesk https://github.com/milu001/sundeskQ
- securreCRT: https://github.com/depau/shcrt
- xshell:
- https://github.com/HyperSine/how-does-Xmanager-encrypt-password 版本 < 7.0
- https://github.com/RowTeam/SharpDecryptPwd 本地解密
- https://github.com/JDArmy/SharpXDecrypt
哈希破解 NTLM Cracking
- NetNTLMv1: https://ntlmv1.com/ 在线破解
- LM + NTLM hashes and corresponding plaintext passwords:
- https://openwall.info/wiki/_media/john/pw-fake-nt.gz 3107
- https://openwall.info/wiki/_media/john/pw-fake-nt100k.gz 100k
后渗透 Post Exploitation
综合工具 Nice Tools
- https://github.com/rapid7/metasploit-framework
- https://github.com/byt3bl33d3r/CrackMapExec 👍
- https://github.com/Pennyw0rth/NetExec
- https://github.com/fortra/impacket 👍
- https://github.com/ghost-ng/slinger 轻量级 impacket 命令行工具,单会话整合多种实用功能
- https://github.com/XiaoliChan/wmiexec-Pro 基于 wmiexec.py 的免杀执行
- https://docs.microsoft.com/en-us/sysinternals/downloads/pstools
- https://github.com/GhostPack/Rubeus
- https://github.com/Kevin-Robertson/Powermad
- https://github.com/PowerShellMafia/PowerSploit
- https://github.com/k8gege/Ladon
- https://github.com/samratashok/nishang PowerShell 专用
- Cobaltstrike Extensions:
- Awesome CobaltStrike: https://github.com/zer0yu/Awesome-CobaltStrike
- Erebus: https://github.com/DeEpinGh0st/Erebus
- LSTAR: https://github.com/lintstar/LSTAR
- ElevateKit: https://github.com/rsmudge/ElevateKit
- C2ReverseProxy: https://github.com/Daybr4ak/C2ReverseProxy
- pystinger: https://github.com/FunnyWolf/pystinger
二进制库 Binaries and Libraries
- LOLBAS: https://github.com/LOLBAS-Project/LOLBAS-Project.github.io Windows 自带二进制与脚本
- GTFOBins: https://github.com/GTFOBins/GTFOBins.github.io Unix 二进制利用
权限维持 Persistence
内存马 MemShell
- https://github.com/pen4uin/java-memshell-generator 👍
- https://github.com/ReaJason/MemShellParty
- https://github.com/BeichenDream/GodzillaMemoryShellProject
- https://github.com/1ucky7/jmg-for-Godzilla
- https://github.com/X1r0z/Godzilla-Suo5MemShell
- https://github.com/tennc/webshell
- https://github.com/novysodope/RMI_Inj_MemShell
- https://github.com/ce-automne/TomcatMemShell
- https://github.com/veo/wsMemShell
Webshell 管理 Webshell Management
- https://github.com/rebeyond/Behinder
- https://github.com/BeichenDream/Godzilla
- https://github.com/shack2/skyscorpion
Webshell 免杀 Webshell Bypass
- https://github.com/AabyssZG/WebShell-Bypass-Guide
- http://bypass.tidesec.com/web/
- https://github.com/cseroad/Webshell_Generate
反弹 Shell 管理 Reverse Shell Management
- https://github.com/WangYihang/Platypus
- https://github.com/calebstewart/pwncat Python 3.9+
权限提升 Privilege Escalation
Linux 本地枚举 Linux Local Enumeration
- https://github.com/carlospolop/privilege-escalation-awesome-scripts-suite
- https://github.com/mostaphabahadou/postenum
- https://github.com/rebootuser/LinEnum
- https://github.com/carlospolop/PEASS-ng/releases/latest/download/linpeas.sh
- https://github.com/DominicBreuker/pspy 无 root 监控 Linux 进程
Windows 本地枚举 Windows Local Enumeration
- https://github.com/S3cur3Th1sSh1t/WinPwn
- https://github.com/carlospolop/PEASS-ng/blob/master/winPEAS/winPEASbat/winPEAS.bat
- https://github.com/S3cur3Th1sSh1t/PowerSharpPack
- https://github.com/Flangvik/SharpCollection
- https://github.com/PowerShellMafia/PowerSploit/blob/dev/Recon/PowerView.ps1
- https://github.com/dafthack/DomainPasswordSpray
- https://github.com/dafthack/MailSniper
Windows 提权 Windows Exploits
- https://github.com/bitsadmin/wesng
- https://github.com/AonCyberLabs/Windows-Exploit-Suggester
- https://github.com/SecWiki/windows-kernel-exploits
- https://github.com/Al1ex/WindowsElevation
- https://i.hacking8.com/tiquan/ online
- https://github.com/BeichenDream/BadPotato/
- https://github.com/giuliano108/SeBackupPrivilege
- https://github.com/gtworek/PSBits/blob/master/Misc/EnableSeBackupPrivilege.ps1
- https://github.com/itm4n/PrivescCheck
- https://github.com/peass-ng/PEASS-ng/blob/master/winPEAS/winPEASexe/README.md
- https://github.com/Ascotbe/Kernelhub
Linux 提权 Linux Exploits
- https://github.com/The-Z-Labs/linux-exploit-suggester
- https://github.com/InteliSecureLabs/Linux_Exploit_Suggester
- https://github.com/liamg/traitor
- https://github.com/peass-ng/PEASS-ng/tree/master/linPEAS
数据库提权 Database Exploits
- https://github.com/Hel10-Web/Databasetools
防御规避 Defense Evasion
Linux 防御规避 Linux Defense Evasion
- libprocesshider: https://github.com/gianlucaborello/libprocesshider 使用 ld 预加载隐藏 Linux 进程
- Linux Kernel Hacking: https://github.com/xcellerator/linux_kernel_hacking
- tasklist /svc && ps -aux: https://tasklist.ffffffff0x.com/
Windows 防御规避 Windows Defense Evasion
- yetAnotherObfuscator: https://github.com/0xb11a1/yetAnotherObfuscator
- hoaxshell: https://github.com/t3l3machus/hoaxshell
- bypassAV: https://github.com/pureqh/bypassAV
- GolangBypassAV: https://github.com/safe6Sec/GolangBypassAV
- BypassAntiVirus: https://github.com/TideSec/BypassAntiVirus
- AV_Evasion_Tool: https://github.com/1y0n/AV_Evasion_Tool
- shellcodeloader: https://github.com/knownsec/shellcodeloader
- tasklist/systeminfo: https://www.shentoushi.top/av/av.php
- rpeloader: https://github.com/Teach2Breach/rpeloader 在没有安装的情况下在 Windows 上使用 Python
内网穿透 Proxy
代理客户端 Proxy Client
- Proxifier: https://www.proxifier.com/
- Proxychains: https://github.com/haad/proxychains
代理工具 Proxy Tools
- frp: https://github.com/fatedier/frp
- frpModify: https://github.com/uknowsec/frpModify
- suo5: https://github.com/zema1/suo5
- Stowaway: https://github.com/ph4ntonn/Stowaway
- Neo-reGeorg: https://github.com/L-codes/Neo-reGeorg
- nps: https://github.com/ehang-io/nps
- reGeorg: https://github.com/sensepost/reGeorg
- rakshasa: https://github.com/Mob2003/rakshasa
- Viper: https://github.com/FunnyWolf/Viper
- ligolo-ng: https://github.com/nicocha30/ligolo-ng TUN 接口
- gost: https://github.com/ginuerzh/gost
DNS 隧道 DNS Tunnel
- iodine: https://github.com/yarrick/iodine
- dnscat2: https://github.com/iagox86/dnscat2
- DNS-Shell: https://github.com/sensepost/DNS-Shell
ICMP 隧道 ICMP Tunnel
- icmpsh: https://github.com/bdamele/icmpsh
端口转发 Port Forwarding
- tcptunnel: https://github.com/vakuum/tcptunnel 内网 → dmz → 攻击机
操作安全 Operation Security
- https://privacy.sexy/ 在 Windows、macOS、Linux 上强化隐私与安全最佳实践
- https://transfer.sh/ 匿名文件传输
- https://a.f8x.io/ 短链接服务
域渗透 Active Directory Penetration
域内信息收集 Collection and Discovery
- BloodHound:
- https://github.com/SpecterOps/BloodHound
- https://github.com/dirkjanm/BloodHound.py
- https://github.com/BloodHoundAD/SharpHound
- https://github.com/CompassSecurity/BloodHoundQueries
- https://github.com/SpecterOps/BloodHound-Legacy/blob/master/Collectors/SharpHound.ps1
- https://github.com/AD-Security/AD_Miner
- https://github.com/NH-RED-TEAM/RustHound
- https://github.com/FalconForceTeam/SOAPHound
- https://github.com/lzzbb/Adinfo
- https://github.com/wh0amitz/SharpADWS 基于 Active Directory Web Services (ADWS) 协议
- LDAP:
- https://github.com/franc-pentest/ldeep
- https://github.com/dirkjanm/ldapdomaindump
- https://github.com/yaap7/ldapsearch-ad
- DNS:
- https://github.com/dirkjanm/adidnsdump
- SCCM:
- https://github.com/garrettfoster13/sccmhunter
- https://github.com/Mayyhem/SharpSCCM
- Brute force users:
- https://github.com/ropnop/kerbrute
域内权限提升 Privilege Escalation
- https://github.com/CravateRouge/bloodyAD
域内漏洞利用 Known Exploited Vulnerabilities
MS14-068
- https://github.com/SpiderLabs/Responder/blob/master/tools/FindSMB2UPTime.py
- https://github.com/SecWiki/windows-kernel-exploits/blob/master/MS14-068/pykek/ms14-068.py
- https://github.com/fortra/impacket/blob/master/examples/goldenPac.py
noPac
CVE-2021-42278/CVE-2021-42287
- https://github.com/Ridter/noPac
- https://github.com/Amulab/advul
Zerologon
CVE-2020-1472
- https://github.com/SecuraBV/CVE-2020-1472/blob/master/zerologon_tester.py
- https://github.com/XiaoliChan/zerologon-Shot
- https://github.com/dirkjanm/CVE-2020-1472
- https://github.com/Potato-py/Potato/tree/03c3551e4770db440b27b0a48fc02b0a38a1cf04/exp/cve/CVE-2020-1472
- https://github.com/risksense/zerologon
- https://github.com/StarfireLab/AutoZerologon
ProxyLogon/ProxyShell
CVE-2021-34473
- https://github.com/dirkjanm/privexchange/
- https://github.com/Jumbo-WJB/PTH_Exchange
- https://github.com/hausec/ProxyLogon
- https://github.com/dmaasland/proxyshell-poc/blob/main/proxyshell_rce.py
ProxyNotShell
CVE-2022-41040/CVE-2022-41082
- https://github.com/testanull/ProxyNotShell-PoC
Printnightmare
CVE-2021-34527/CVE-2021-1675
- https://github.com/cube0x0/CVE-2021-1675
- https://github.com/nemo-wq/PrintNightmare-CVE-2021-34527
- https://github.com/calebstewart/CVE-2021-1675
域内渗透方式 Methodology
Coerce and Relay
- PetitPotam: https://github.com/topotam/PetitPotam
- PrinterBug: https://github.com/leechristensen/SpoolSample
- DFSCoerce: https://github.com/Wh04m1001/DFSCoerce
- WSPCoerce: https://github.com/slemire/WSPCoerce
- ShadowCoerce: https://github.com/ShutdownRepo/ShadowCoerce
- PrivExchange: https://github.com/dirkjanm/privexchange/
- Coercer: https://github.com/p0dalirius/Coercer
- cannon: https://github.com/Amulab/cannon
- Responder: https://github.com/lgandx/Responder
- Responder-Windows: https://github.com/lgandx/Responder-Windows
- KrbRelayUp: https://github.com/Dec0ne/KrbRelayUp
- ntlmrelayx: https://github.com/fortra/impacket/blob/master/examples/ntlmrelayx.py
- kerbrelayx: https://github.com/dirkjanm/krbrelayx
Delegation
- findDelegation: https://github.com/fortra/impacket/blob/master/examples/findDelegation.py
- Impacket rbcd.py: https://github.com/fortra/impacket/blob/master/examples/rbcd.py
- SharpRBCD: https://github.com/Kryp7os/SharpRBCD
- PowerView: https://github.com/PowerShellMafia/PowerSploit/blob/dev/Recon/PowerView.ps1
- Delegations: https://github.com/TheManticoreProject/Delegations
ADCS
Active Directory Certificate Services
- Active Directory Certificate Services(AD CS) 枚举与利用:
- Certify: https://github.com/GhostPack/Certify
- Certipy: https://github.com/ly4k/Certipy
- certi: https://github.com/zer1t0/certi
- PKINITtools: https://github.com/dirkjanm/PKINITtools
- ADCSPwn: https://github.com/bats3c/ADCSPwn
- PassTheCert: https://github.com/AlmondOffSec/PassTheCert
ACLs and ACEs
- https://github.com/n00py/DCSync
- https://github.com/ShutdownRepo/pywhisker
- https://github.com/ShutdownRepo/targetedKerberoast
防御性安全 Blue Teaming and Defensive Security
内存马查杀 Memshell Detection
- https://github.com/LandGrey/copagent
- https://github.com/alibaba/arthas
- https://github.com/c0ny1/java-memshell-scanner
- https://github.com/yzddmr6/ASP.NET-Memshell-Scanner
Webshell 查杀 Webshell Detection
- https://webshellchop.chaitin.cn/demo/
- http://www.shellpub.com
- https://github.com/jvoisin/php-malware-finder
- https://www.d99net.net/
攻击研判 Blue Teaming
- CobaltStrike Decrypt: https://github.com/5ime/CS_Decrypt
- BlueTeamTools: https://github.com/abc123info/BlueTeamTools
- IP Logger: https://iplogger.org/ 记录并追踪 IP 地址
基线加固 Enforcement
- https://github.com/AV1080p/Benchmarks
- https://github.com/xiaoyunjie/Shell_Script
应急响应 Incident Response
- https://github.com/grayddq/GScan
- https://github.com/ppabc/security_check
- https://github.com/T0xst/linux
- https://github.com/al0ne/LinuxCheck
勒索病毒 Ransomware
搜索引擎 Search Engine
- 360: http://lesuobingdu.360.cn
- 腾讯: https://guanjia.qq.com/pr/ls
- 启明星辰: https://lesuo.venuseye.com.cn
- 奇安信: https://lesuobingdu.qianxin.com
- 深信服: https://edr.sangfor.com.cn/#/information/ransom_search
解密工具 Decryption Tools
- 腾讯: https://habo.qq.com/tool
- 金山毒霸: http://www.duba.net/dbt/wannacry.html
- 瑞星: http://it.rising.com.cn/fanglesuo/index.html
- 卡巴斯基: https://noransom.kaspersky.com/
- https://www.nomoreransom.org/zh/index.html
- https://id-ransomware.malwarehunterteam.com
- https://www.avast.com/ransomware-decryption-tools
- https://www.emsisoft.com/en/ransomware-decryption/
- https://github.com/jiansiting/Decryption-Tools
开源蜜罐 Open-Source Honeypot
- awesome-honeypots: https://github.com/paralax/awesome-honeypots 蜜罐资源汇总列表
- HFish: https://github.com/hacklcx/HFish
- conpot: https://github.com/mushorg/conpot 工业控制系统(ICS)专用蜜罐
- MysqlHoneypot: https://github.com/qigpig/MysqlHoneypot 基于 MySQL 蜜罐获取微信号
- Ehoney: https://github.com/seccome/Ehoney
逆向工程 Reverse Engineering
综合工具 Nice Tools
- OpenArk: https://github.com/BlackINT3/OpenArk 反 Rootkit 工具
- python arsenal for RE: https://pythonarsenal.com/ 逆向工程工具集
- IDA Pro: https://hex-rays.com/ida-pro/
- IDA Pro MCP: https://github.com/mrexodia/ida-pro-mcp 集成 AI 的 IDA Pro 工具
- Angr: https://github.com/angr/angr 二进制分析平台
- Cutter: https://cutter.re/ 开源逆向工程平台
- UPX: https://github.com/upx/upx
静态分析 Static Analysis
- checksec: https://github.com/slimm609/checksec
- Detect-It-Easy: https://github.com/horsicq/Detect-It-Easy
- ExeinfoPE: https://github.com/ExeinfoASL/ASL
- PEiD: https://www.aldeid.com/wiki/PEiD
- bindiff: https://www.zynamics.com/software.html
- 在线编译器: https://godbolt.org/
动态调试 Dynamic Analysis
- Ollydbg: https://www.ollydbg.de/
- x64dbg: https://x64dbg.com/
Java
- jadx: https://github.com/skylot/jadx
- JEB: https://www.pnfsoftware.com/
- GDA: https://github.com/charles2gan/GDA-android-reversing-Tool
- jd-gui: https://github.com/java-decompiler/jd-gui
- jar-analyzer: https://github.com/jar-analyzer/jar-analyzer/
Mobile
- scrcpy: https://github.com/Genymobile/scrcpy
- android-reverse: https://github.com/WuFengXue/android-reverse
Python
- py2exe: https://www.py2exe.org/ py->exe
- pyinstaller: https://github.com/pyinstaller/pyinstaller py->exe
- unpy2exe: https://github.com/matiasb/unpy2exe exe->pyc
- pyinstxtractor: https://github.com/extremecoders-re/pyinstxtractor exe->pyc
- pycDcode: https://github.com/rocky/python-uncompyle6/ pyc->py
- pycDcode: https://github.com/BarakAharoni/pycDcode
Rust/Go/.NET
- https://github.com/cha5126568/rust-reversing-helper for rust
- https://github.com/strazzere/golang_loader_assist for golang
- https://github.com/sibears/IDAGolangHelper for golang
- https://www.jetbrains.com/zh-cn/decompiler/ for .NET
- https://github.com/dnSpy/dnSpy for .NET
JavaScript
- https://github.com/0xsdeo/AntiDebug_Breaker
- https://github.com/jxhczhl/JsRpc
云安全 Cloud Security
开源资源 Resources
- TeamsSix:
- https://github.com/teamssix/awesome-cloud-security
- https://wiki.teamssix.com/
- lzCloudSecurity:
- https://github.com/EvilAnne/lzCloudSecurity
- https://lzcloudsecurity.gitbook.io/yun-an-quan-gong-fang-ru-men/
- CSA Research: https://c-csa.cn/research/results/
- HackTricks Cloud: https://cloud.hacktricks.xyz/
- Awesome-CloudSec-Labs: https://github.com/iknowjason/Awesome-CloudSec-Labs
- Aliyun OpenAPI: https://next.api.aliyun.com/api/
- Cloud Native Landscape: https://landscape.cncf.io/
- Cloud Vulnerabilities and Security Issues Database: https://www.cloudvulndb.org/ 云漏洞与安全问题数据库
云安全矩阵 Cloud Threat Matrix
- https://attack.mitre.org/matrices/enterprise/cloud/
- https://cloudsec.huoxian.cn/
- https://cloudsec.tencent.com/home/
- https://owasp.org/www-project-kubernetes-top-ten/ OWASP Kubernetes 十大风险 - 2022 版
- https://www.microsoft.com/en-us/security/blog/2021/03/23/secure-containerized-environments-with-updated-threat-matrix-for-kubernetes/ Kubernetes 威胁矩阵
云服务 Cloud Services
三大云服务提供商: - Amazon Web Services (AWS) / Microsoft Azure / Google Cloud Platform (GCP) - 阿里云 / 腾讯云 / 华为云
云管平台 Management Tools
- https://yun.cloudbility.com/ 云存储图形化管理平台
- https://github.com/aliyun/aliyun-cli 适用于阿里云 OSS
- https://github.com/aliyun/oss-browser 基于阿里云 CLI 的图形化工具
- https://github.com/TencentCloud/cosbrowser 适用于腾讯云 COS
- https://github.com/TencentCloud/tencentcloud-cli 基于腾讯云 CLI
- https://support.huaweicloud.com/browsertg-obs/obs_03_1003.html 适用于华为云 OBS
- https://www.ctyun.cn/document/10000101/10006768 适用于天翼云 OBS
- https://www.ctyun.cn/document/10306929/10132519 适用于天翼云媒体服务
- https://docsv4.qingcloud.com/user_guide/development_docs/cli/install/install/ 基于青云 CLI
- https://github.com/qiniu/kodo-browser 适用于七牛云 OSS
AK/SK 利用 AK/SK Exploit
- https://wiki.teamssix.com/cf/ 漏洞利用框架 v0.5.0(开源)
- https://github.com/wgpsec/cloudsword 云服务安全测试工具
- https://github.com/CloudExplorer-Dev/CloudExplorer-Lite fit2cloud 云资源管理工具
- https://github.com/mrknow001/aliyun-accesskey-Tools 阿里云 AccessKey 专用工具
- https://github.com/iiiusky/alicloud-tools 阿里云安全工具集
- https://github.com/NS-Sp4ce/AliyunAccessKeyTools 阿里云 AccessKey 利用工具
- https://github.com/freeFV/Tencent_Yun_tools 腾讯云安全工具集
- https://github.com/libaibaia/cloudSec 支持三大云 + AWS/七牛云的 Web 工具
- https://github.com/wyzxxz/aksk_tool 支持三大云 + AWS/优刻得/京东云/百度云/七牛云
- https://github.com/UzJu/Cloud-Bucket-Leak-Detection-Tools 云存储桶泄露检测工具
- https://github.com/dark-kingA/cloudTools 支持三大云 + 优刻得的安全工具
云原生 Cloud Native
综合工具 Nice Tools
- https://github.com/HummerRisk/HummerRisk 开源云原生安全平台
容器 Docker
- https://github.com/wagoodman/dive 探索 Docker 镜像各层结构
- https://github.com/docker/docker-bench-security Docker 安全基准测试工具
- https://github.com/eliasgranderubio/dagda/ Docker 镜像/容器静态分析工具(检测漏洞、木马、病毒等恶意威胁)
- https://github.com/teamssix/container-escape-check 容器逃逸检测工具
- https://github.com/brant-ruan/awesome-container-escape 容器逃逸技术汇总
- https://github.com/cdk-team/CDK 容器渗透测试工具包
- https://github.com/chaitin/veinmind-tools 容器安全工具集
集群 Kubernetes
- https://kubernetes.io/docs/tasks/tools/ Kubernetes 官方工具文档
- https://github.com/etcd-io/etcd 分布式键值存储(K8s 核心组件)
- https://github.com/kubernetes/minikube 本地 Kubernetes 集群搭建工具
- https://github.com/kubernetes-sigs/kind 基于 Docker 的本地 Kubernetes 集群工具
- https://github.com/kubernetes/kubeadm 生产/测试环境 Kubernetes 集群部署工具
- https://github.com/kubernetes-sigs/cri-tools Kubelet 容器运行时接口(CRI)工具集
- https://github.com/derailed/k9s Kubernetes 终端管理 CLI 工具
- https://github.com/lightspin-tech/red-kube 基于 kubectl 的红队 K8s 对抗模拟工具
- https://github.com/DataDog/KubeHound Kubernetes 攻击路径自动化分析工具
- https://github.com/inguardians/peirates Kubernetes 渗透测试工具
- https://github.com/docker/docker-bench-security Docker CIS 基准测试分析工具
- https://github.com/aquasecurity/kube-bench Kubernetes CIS 基准测试分析工具
- https://github.com/aquasecurity/kube-hunter Kubernetes 安全弱点探测工具
提高生产力的使用姿势
如何快速使用 alias
Windows 创建 alias.bat,激活 conda 虚拟环境,在隔离环境下运行程序或工具。双击 alias.bat,重启 cmd,配置生效。
@echo off
:: Software
@DOSKEY ida64=activate base$t"D:\CTFTools\Cracking\IDA_7.7\ida64.exe"

:: Tools
@DOSKEY fscan=cd /d D:\Software\HackTools\fscan$tactivate security$tdir
将 alias.bat 配置为开机自启动:
- 注册表进入
计算机\HKEY_CURRENT_USER\Software\Microsoft\Command Processor; - 创建字符串值
autorun,赋值为 alias.bat 所在位置,例如D: \Software\alias.bat; - 重启系统,配置生效。
MacOS 编辑 .zshrc,重启 shell,配置生效:
# 3. Control and Command
alias behinder="cd /Users/threekiii/HackTools/C2/Behinder_v4.1/ && /Library/Java/JavaVirtualMachines/jdk-1.8.jdk/Contents/Home/bin/java -jar Behinder.jar "
alias godzilla="cd /Users/threekiii/HackTools/C2/Godzilla_v4.0.1/ && /Library/Java/JavaVirtualMachines/jdk-1.8.jdk/Contents/Home/bin/java -jar godzilla.jar "
如何优化原生终端
Windows 通过 tabby + clink 优化原生终端,实现命令自动补全、vps ssh/ftp/sftp、输出日志记录等功能:
- warp: https://github.com/warpdotdev/Warp 👍
- tabby: https://github.com/Eugeny/tabby
- clink: https://github.com/chrisant996/clink
MacOS 通过 warp + ohmyzsh 优化原生终端,warp 自带命令自动补全,引入“块”概念,提供了更现代化的编程体验(Modern UX and Text Editing):
- warp: https://github.com/warpdotdev/Warp 👍
- ohmyzsh: https://github.com/ohmyzsh/ohmyzsh
如何解决终端中文乱码
Windows 注册表进入 计算机\HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Command Processor,创建字符串值 autorun,赋值为 chcp 65001。

Related repositories
Master programming by recreating your favorite technologies from scratch.
A curated meta-list of curated lists organized by technology domain. The repository acts as a directory pointing to hundreds of specialized awesome lists covering programming languages, platforms, frameworks, and tooling. All content is community-contributed under the CC0 public domain dedication.
Public APIs is a community-curated GitHub repository listing free, publicly accessible APIs across a wide range of categories, with auth type, HTTPS, and CORS noted for each entry. It's a browsable reference, not a library to install.
REA is an MCP server and CLI that gives AI coding agents the ability to reverse engineer binaries, JavaScript apps, .NET assemblies, and websites. It hooks into Hopper, Ghidra, or IDA Pro for native binary work, or runs static JavaScript analysis with just Node.js. Every investigation returns an Evidence bundle that includes what was found, what was not, and the reasoning path. Setup registers REA with supported agents and walks you through connecting an analysis engine. The CLI also works standalone for terminal-first workflows.
Quick answers
Does Threekiii/Awesome-Redteam have a project website?
No homepage URL was recorded for Threekiii/Awesome-Redteam in TopGit's last sync. The README tab above frequently contains screenshots and demo links, or check the repository description on GitHub.
How active is development on Threekiii/Awesome-Redteam?
The most recent commit recorded on Threekiii/Awesome-Redteam was 4 months ago, based on the GitHub push timestamp. The repository has 755 forks — one of the better signals of community interest.
Is Threekiii/Awesome-Redteam open source?
TopGit's metadata for Threekiii/Awesome-Redteam does not record a license. Most public repositories on GitHub ARE open source, but the exact terms vary — verify by opening the LICENSE file directly.
What topics is Threekiii/Awesome-Redteam associated with?
GitHub's repository topics for Threekiii/Awesome-Redteam: "command-and-control", "execution", "exploit", "initial-access", "lateral-movement", "privilege-escalation", "reconnaissance", "red-teaming". TopGit's editorial category is open-source.
Where do I read more about Threekiii/Awesome-Redteam?
This TopGit page is a snapshot — the READ ME tab shows the project's own README content (links stripped, images preserved). The GitHub repository at github.com/Threekiii/Awesome-Redteam is the definitive source.
Read full README in the tab above.
Is Awesome-Redteam worth your time?
ChatGPT, Claude and Perplexity can all read this page. Ask one of them what it makes of Awesome-Redteam.